ISO 27001 Consultants in UAE: How to Choose the Right Consultancy for Certification
Information security is now a board-level topic for UAE companies. Customers, banks and government entities increasingly ask suppliers to prove that their data is protected, and ISO/IEC 27001 is the most widely recognised way to do that. Many organisations hire an ISO 27001 consultant to prepare for certification. This guide explains what a consultant does, what to look for, and how consulting differs from the certification audit itself.
What Does an ISO 27001 Consultant Do?
An ISO 27001 consultant helps you design, implement and document an Information Security Management System (ISMS) so that you are ready for the certification audit. Typical work includes:
- Defining the ISMS scope and context of the organisation.
- Running a gap analysis against ISO/IEC 27001:2022 and the Annex A controls.
- Carrying out a risk assessment and preparing the risk treatment plan.
- Writing the Statement of Applicability, policies and procedures.
- Training staff on security awareness and their responsibilities.
- Conducting an internal audit and supporting the management review.
Consultant vs Certification Body: An Important Difference
A consultant prepares you. A certification body audits you and issues the certificate. To protect impartiality, an accredited certification body cannot design your system and then certify it. Always keep these two roles separate, and make sure your consultant does not claim to "guarantee" certification, because the final decision belongs to the certification body.
When Should You Hire a Consultant?
A consultant is useful when:
- You have no in-house person with ISO 27001 experience.
- A customer or tender has set a deadline for certification.
- Your IT environment is complex, with cloud services, multiple sites or outsourced vendors.
- You need to align with UAE data protection and cyber security expectations at the same time.
If you already have a mature security team, you may only need a short gap analysis and internal audit support.
How to Choose an ISO 27001 Consultant in the UAE
- Relevant experience: Ask for examples of ISMS projects in your industry and company size.
- Qualifications: Look for recognised ISO 27001 Lead Implementer or Lead Auditor credentials.
- Clear methodology: A good consultant can explain each phase, deliverable and timeline.
- Your team stays involved: The ISMS must reflect how you really work. Avoid anyone who only hands over generic templates.
- Transparent scope and fees: Get written details of what is included, such as workshops, document support and internal audit.
- Post-certification support: Check whether help is available for surveillance audits and the annual review cycle.
Questions to Ask Before You Hire
- Which version of the standard will you implement, and how will you handle the 2022 control structure?
- How will you involve our IT, HR and management teams?
- What documents will we own at the end of the project?
- How do you prepare us for the Stage 1 and Stage 2 audits?
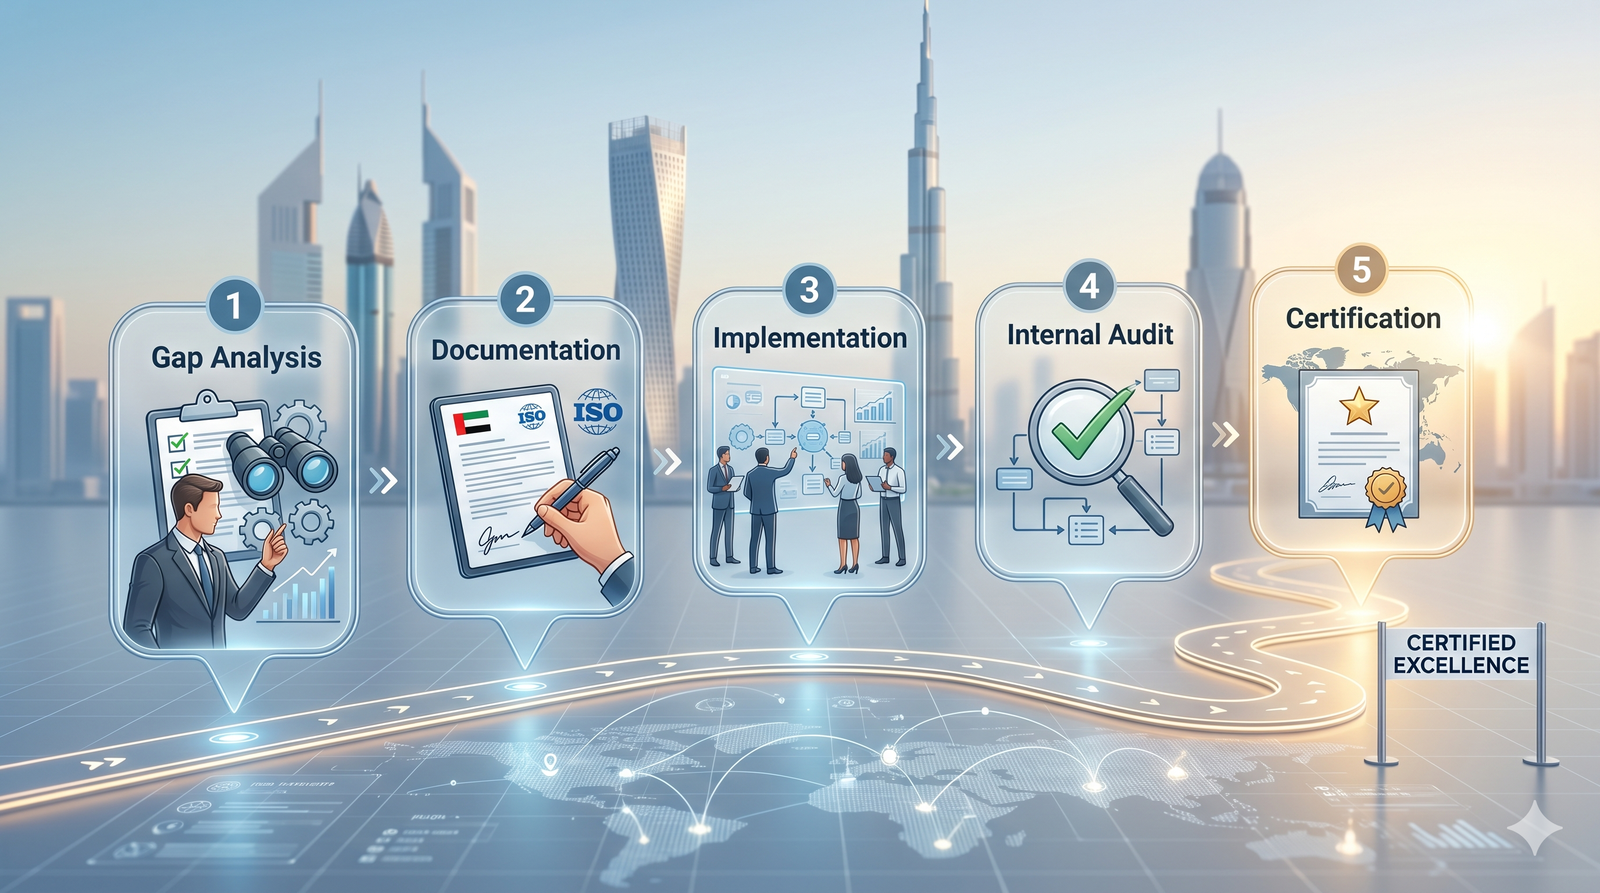
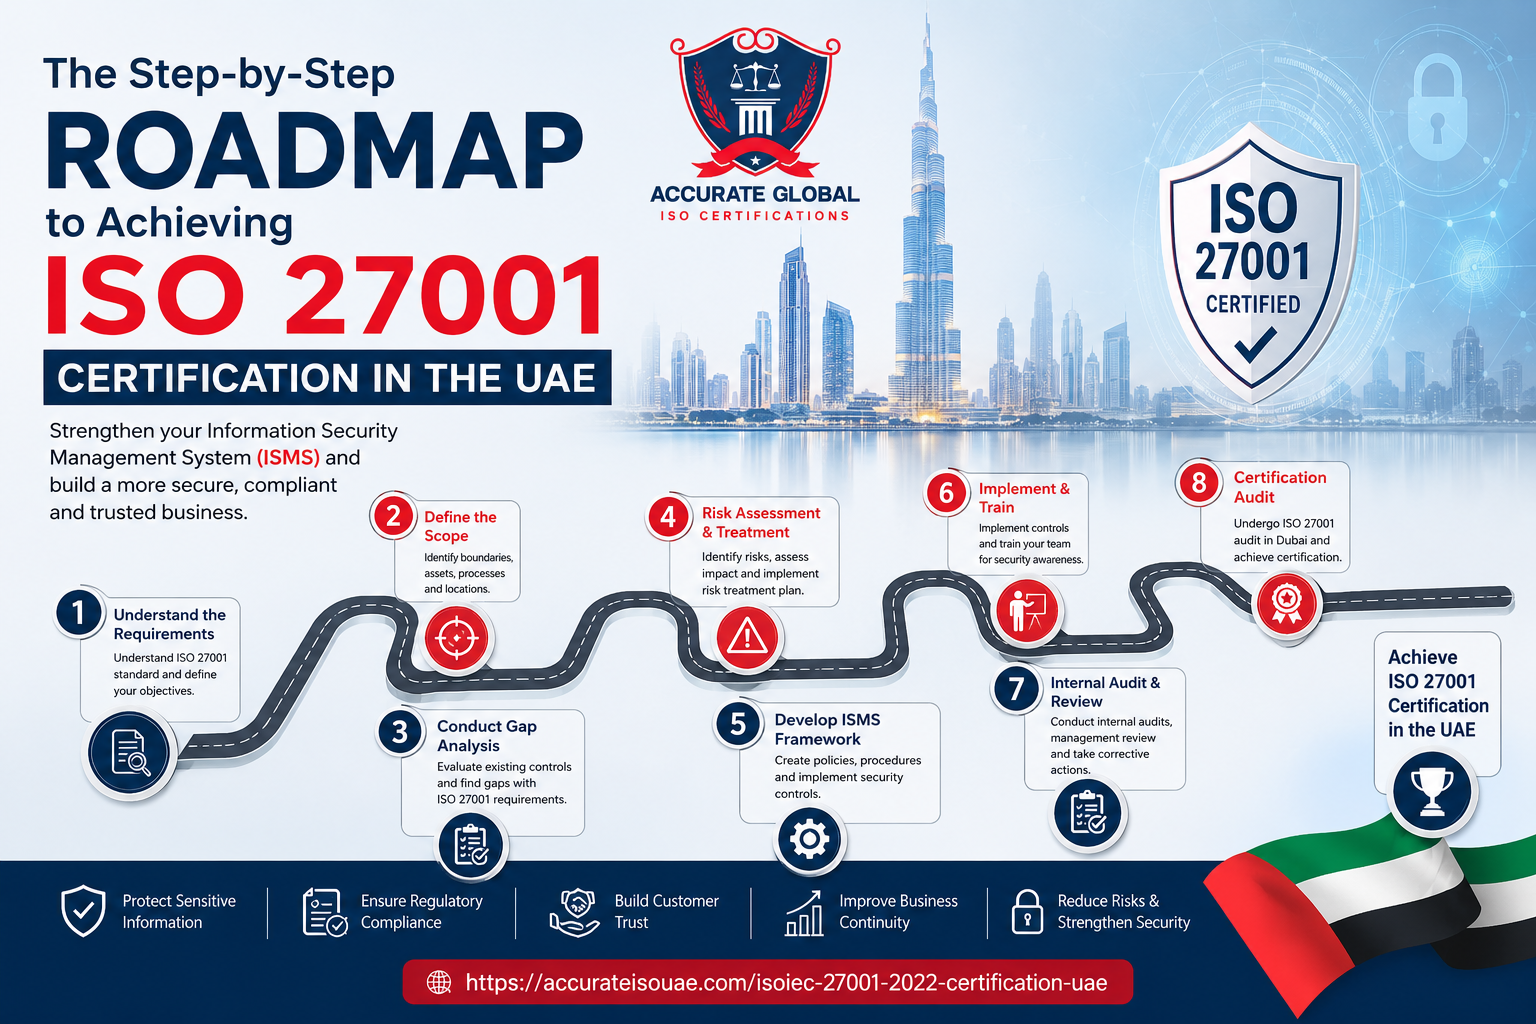
Typical ISO 27001 Implementation Roadmap
- Scope, context and leadership commitment.
- Gap analysis and risk assessment.
- Control implementation and documentation.
- Awareness training and operation of the ISMS.
- Internal audit and management review.
- Stage 1 and Stage 2 certification audits.
For a deeper look at controls and audit readiness, read our guide on ISO 27001 compliance in the UAE.
Next Steps
If you are planning ISO 27001, start with a gap analysis so you know where you stand. Explore our ISO/IEC 27001:2022 certification page to understand the audit requirements, or talk to our team about your scope and timeline.
Frequently Asked Questions
Is a consultant mandatory for ISO 27001?
No. Some organisations implement the standard internally, but a consultant can save time and reduce the risk of audit findings.
How long does ISO 27001 implementation take?
It depends on scope, maturity and available resources. Smaller organisations can be ready in a few months, while complex environments take longer.
Does ISO 27001 replace UAE regulatory compliance?
No. It supports compliance by providing a structured framework, but you must still meet applicable UAE laws and sector regulations.
.png)
.png)
.png)
.png)
.png)
.png)
.png)